Cybersecurity insights on SIEM, IAM, compliance, and managed services.
CERT-In's CISG-2026-02 sets six risk-tiered remediation windows, the tightest 12 hours. What the blueprint says, and how to instrument the SLA.
Most QRadar alternative guides ignore India. A shortlist filtered by data residency, CERT-In retention and SEBI CSCRF — plus when staying on QRadar is right.
RBI's Cybersecurity Directions 2026 took effect immediately on 31 July 2026. What Chapter VI requires on CSOC staffing, and the cadence your board must see.
DPDP Rule 4 commences 13 November 2026, but binds Consent Managers, not ordinary Data Fiduciaries. What the Gazette says and what to build by 13 May 2027.
QRadar SaaS hits end of life on 14 April and 31 August 2026. A decision framework for Indian SOC teams weighing Cortex XSIAM, another SIEM, or on-prem.
QRadar 7.6.0 is GA, the legacy Auto Update server retires 21 August 2026, and several QRadar products hit end of support. A practitioner's upgrade plan.
CERT-In and CSIRT-Fin report that trust-chain attacks have displaced traditional hacking in BFSI. The four gap layers, and the controls that close them.
Avoid common cybersecurity hiring mistakes in India. Learn why 70% of candidates fail technical interviews — and how to fix your hiring process.
Tier-by-tier SEBI CSCRF checklist for FY 2026-27: SOC, CISO governance, VAPT, IAM, DAM and incident response — plus the 5 gaps auditors flag most.
Scale SOC, SIEM, IAM, GRC, and cloud security teams faster with Cyberaube's contract cybersecurity staffing and staff augmentation model.
How to hire permanent SOC, SIEM, IAM, GRC, and security leadership talent in India — role selection, screening, salary benchmarks, and 90-day replacement terms.
SEBI CSCRF by tier: who counts as an MII or Qualified RE, what each must implement, and where BFSI firms most often fall short.
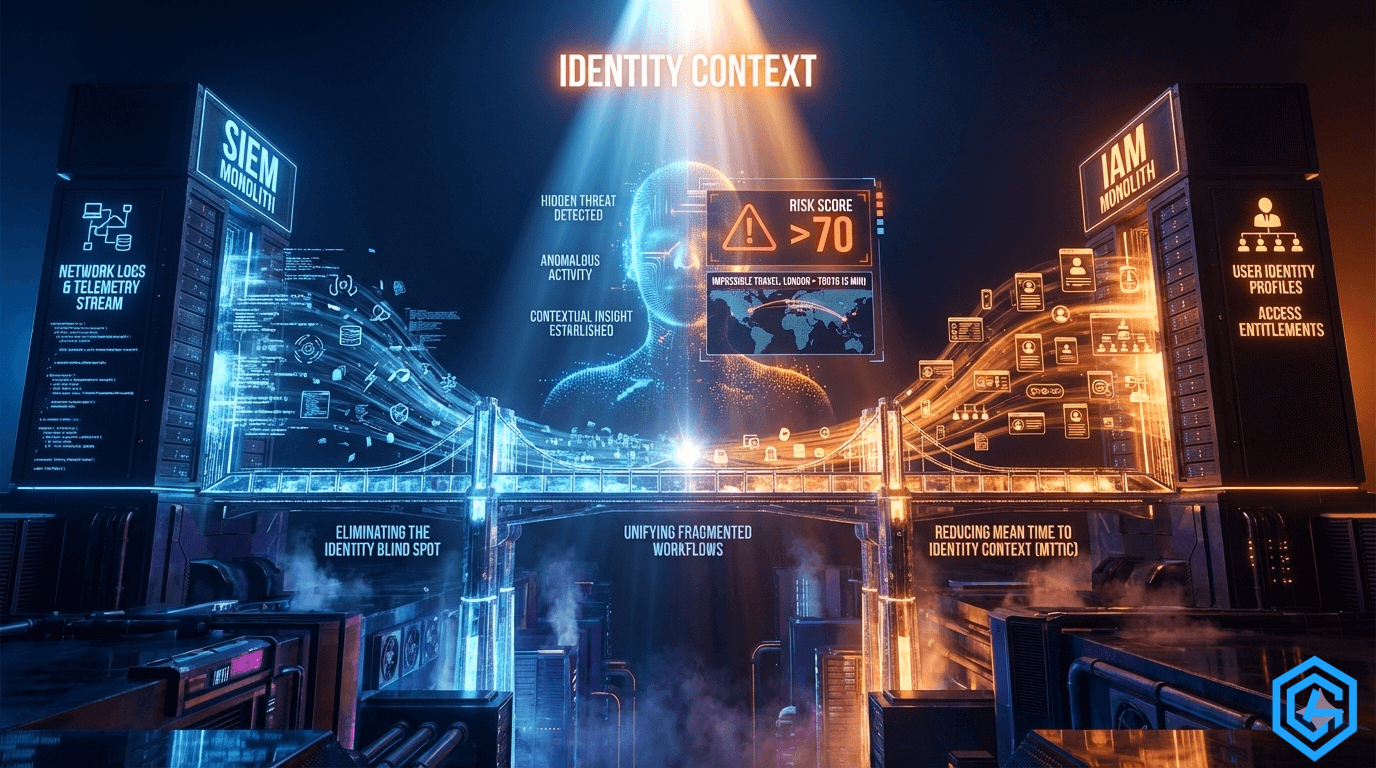
How to integrate SIEM and IAM — architecture patterns, contextual enrichment, and unified identity threat detection with QRadar, Splunk, Okta & CyberArk.
Step-by-step IBM Guardium v12.2.1 roadmap — verified architecture, deployment phases, sizing, and DPDP, SEBI & RBI compliance mapping for enterprises.
SOC as a Service in India: how it works, real INR pricing bands, what to check in a provider, and a framework for in-house vs outsourced.
A practitioner's QRadar vs Splunk comparison: real India pricing (₹30 LPA–₹5 Cr+), detection strengths, cloud options, and a 30-day test to pick your SIEM.
Ten practices for Indian businesses in 2026, each tied to what DPDP, CERT-In, SEBI CSCRF and RBI actually require — not generic advice.
Compare the best DPDP compliance tools and software for 2026 — consent management, data discovery, audit evidence — and how to pick the right platform.